Is Your Cloud Environment Actually Ready for a Real Attack?
Every business running workloads in AWS, Azure, or a hybrid UAE data center eventually asks the same question: if someone tried to break in today, would they get anywhere? That question is exactly why Cloud Security Testing Services in UAE exist not as a checkbox exercise, but as a way to find out, before an attacker does, whether identity controls, storage permissions, and network boundaries actually hold up. For companies in Dubai and Abu Dhabi scaling cloud infrastructure faster than their security reviews can keep pace, this isn’t a theoretical concern it’s an operational one.
What Does Cloud Security Testing Actually Check?
So what does a cloud assessment look at, specifically? It isn’t a generic scan. Cloud Security Testing Services in UAE typically examine identity and access management (IAM) roles, exposed storage buckets, misconfigured security groups, encryption and key handling, and logging gaps that leave attacks invisible until it’s too late. Nathan Labs, through its vaptsecurity.com cloud security testing services, approaches this by validating real attack paths across AWS, Azure, and hybrid setups not just scoring a configuration against a checklist, but showing what an attacker could actually reach if a misconfiguration were exploited.
This distinction matters. A posture score tells you something is misconfigured. A tested attack path tells you what happens next whether that misconfiguration leads to data exposure, privilege escalation, or lateral movement across connected systems.
Why Should UAE Businesses Test Cloud Resilience Now?
Why now, specifically? Because cloud adoption in the UAE has reached a point where infrastructure changes faster than internal review cycles. Teams across DIFC, Business Bay, Dubai Internet City, and Abu Dhabi’s ADGM are spinning up new services, APIs, and storage weekly. Each change is a potential new entry point, and most cloud breaches don’t involve sophisticated hacking at all they involve an overly permissive IAM role, a public bucket, or a monitoring gap nobody noticed.
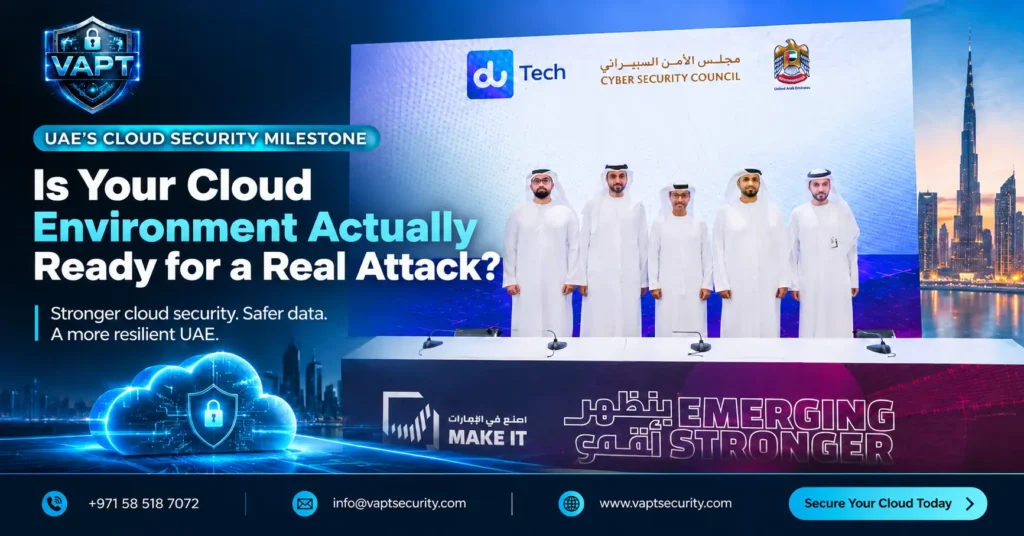
There’s also a broader national context worth noting here. In May 2026, the UAE Cyber Security Council certified du Tech’s National Hypercloud against the National Cloud Security Policy a certification focused on data residency, protection standards, and secure cloud infrastructure for government and enterprise workloads. It’s a cloud-security development, not a breach, but it reflects something relevant: the UAE is actively formalizing what “secure cloud” means at a national level, and that raises the baseline expectation for any organization running workloads locally, including those not on a sovereign platform.
What Gets Tested in a Cloud Security Assessment?
What exactly falls under scope? A structured assessment generally covers five layers: identity and access review (privilege design, MFA enforcement, stale accounts), storage and data exposure testing (public access checks, object-level permissions), network and perimeter validation (security group rules, segmentation), workload and configuration testing (container hardening, serverless exposure), and logging/monitoring readiness (what’s actually being alerted on versus what’s silently happening).
This is where Cloud Security Assessment in UAE work differs from a basic compliance scan each layer is tested for exploitability, not just flagged as a finding. A related but distinct discipline, Cloud Penetration Testing Services, goes a step further by simulating how an attacker would chain these weaknesses together to reach sensitive data or admin functions.
How Does Controlled Cloud Testing Actually Work?
How is this run without disrupting live operations? A typical engagement starts with scope definition which cloud accounts, regions, and services matter most for data protection or uptime. From there, testing combines configuration review with practical attack-path validation, followed by a prioritized report that separates critical risks from low-impact noise. The cycle closes with retesting, confirming that fixes actually hold rather than assuming they do.
For organizations running APIs alongside their cloud workloads, this often overlaps with API security testing in UAE, since many cloud-hosted services expose data through APIs that carry their own authentication and rate-limiting risks. And because fixes aren’t always applied correctly the first time, vulnerability retesting services in UAE play a direct role in confirming closure rather than leaving issues open indefinitely.
What Weaknesses Show Up Most Often?
What do these assessments typically find? Repeat patterns are common: IAM roles with far more access than needed, storage buckets left publicly readable, security groups with wide-open inbound rules, hardcoded credentials in code repositories, and logging that exists on paper but doesn’t actually trigger alerts. None of these require advanced exploitation skills they’re often the result of fast-moving deployment cycles outpacing review.
FAQ
Is Cloud Security Testing the same as a compliance audit?
No. A compliance audit checks against a standard’s checklist. Cloud security testing validates whether real attack paths exist and whether misconfigurations are exploitable compliance can follow from this, but it isn’t the starting point.
How often should UAE businesses test their cloud environment?
Given how frequently cloud configurations change new services, new access keys, new integrations testing on a regular cycle rather than once a year gives a more accurate picture of current risk.
Does this cover AWS, Azure, and hybrid setups?
Yes, assessments are generally scoped to the platform(s) in use, whether that’s a single provider, multi-cloud, or hybrid infrastructure connecting on-prem and cloud resources.
What’s the difference between Cloud Security Testing and Cloud Penetration Testing?
Cloud Security Testing reviews configurations and controls broadly. Cloud Penetration Testing Services simulate real attacker behavior to prove whether a specific weakness can actually be exploited.
Does a national certification like du Tech’s National Hypercloud mean individual businesses don’t need their own testing?
No a platform-level certification addresses the underlying infrastructure’s compliance with national policy. Individual applications, APIs, and configurations built on top of any cloud platform still need their own independent validation.
Thinking About Your Own Cloud Exposure?
If you’re unsure what your current cloud setup would reveal under real testing conditions, that’s worth a direct conversation rather than a guess. Nathan Labs’ Cloud Security Testing Services in UAE are built around exactly this kind of practical validation.
Contact:
📞 +971 58 518 7072
📧 info@vaptsecurity.com
🌐 www.vaptsecurity.com